Skip to content
Claim this template

Free course template · Global

Cyber risk governance for managers and boards

A ready-made course, live deck and two surveys for executives. 40 minutes, 6 lessons. Last reviewed 21 October 2026; not legal advice.

Claim the templatePreview the courseDownload SCORM for your LMS

Free. No credit card. Edit everything.

Play a game from the course

Cyber risk governance for managers and boards: try 3 questions

Three questions from this course. Pick an answer, then see why.

Play the game

Game not loading? Open it in a new tab (opens in a new tab)

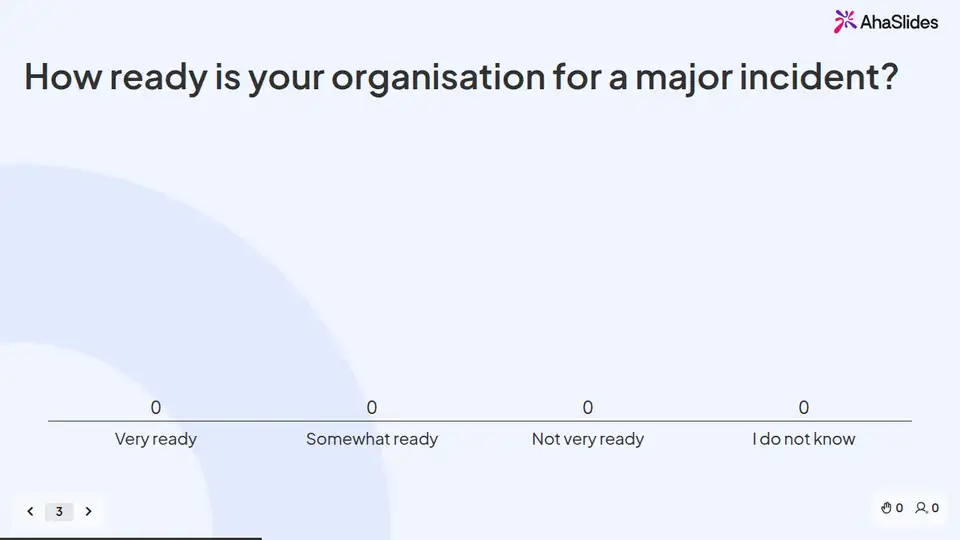
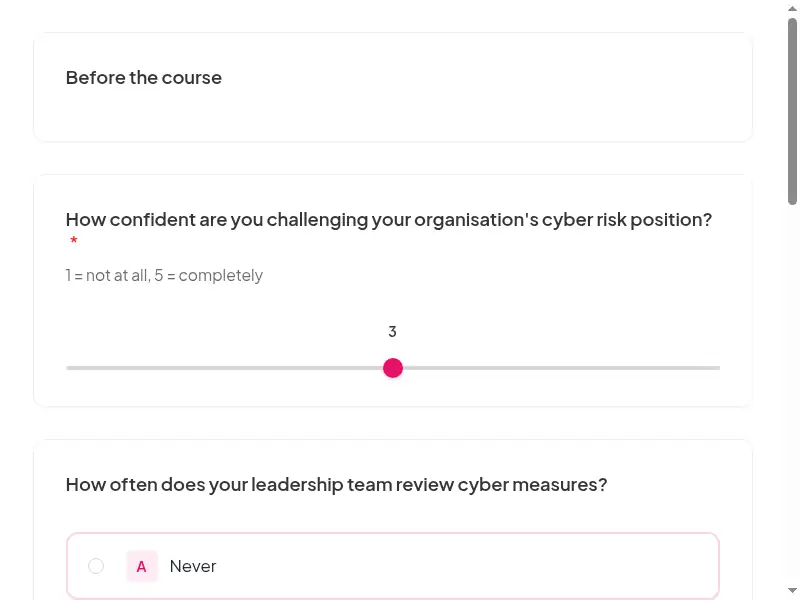
Three pieces that work together

Learners sign in, so every finish and score is recorded. 9 fields to fill in with your details.
Claim the template
The Cyber risk governance for managers and boards course as a learner first sees it

6 lessons, about 40 minutes

Minutes are an estimate.

  • Lesson 1: Cyber risk is business risk · 7 min

    Before you begin · The Monday morning call · Who owns this?

  • Lesson 2: Five questions for your organisation · 7 min

    The questions · Good answers · Check

  • Lesson 3: Risk appetite and measures · 7 min

    Appetite · A short dashboard · Try it

  • Lesson 4: Grey areas: paying, telling and trade-offs · 7 min

    Decisions in a crisis · What would you do? · Check

  • Lesson 5: Duties and standards · 7 min

    Where duties come from · Your markets · Try it

  • Lesson 6: Your leadership actions and the final assessment · 5 min

    Next steps · Practice

Claim the template

Inside this course

Taken from the course itself.

By the end, learners can

  • Explain cyber risk as a business risk the board and leaders own
  • Ask the five questions that show how exposed the organisation is
  • Set a risk appetite and read a small set of cyber measures
  • Describe leaders' role before, during and after a major incident
  • Know which laws and standards bring duties for leaders in your markets

Sample questions, with answers

  1. Redhill Works' systems are down. Who must decide how the business responds?

    • Leaders, with specialist advice
    • IT alone
    • The supplier
    • The insurer

    Answer: Leaders, with specialist advice. Leaders own the business decisions. Specialists, suppliers and insurers inform them but cannot decide for you.

    Lesson 1: Cyber risk is business risk

  2. A dashboard shows hundreds of measures. What is the best fix?

    • Cut it to a few measures read regularly
    • Add more measures
    • Hide the red ones
    • Ask IT to explain every month

    Answer: Cut it to a few measures read regularly. A short dashboard that is read often leads to action. A long one is ignored.

    Lesson 3: Risk appetite and measures

  3. What is the best proof that you meet a standard?

    • The official certificate and its scope
    • A confident answer
    • A promise to apply
    • A slide from sales

    Answer: The official certificate and its scope. A certificate shows which parts of the organisation are covered. Always check the scope.

    Lesson 5: Duties and standards

A scenario from "Risk appetite and measures"

The dashboard shows patching is 60% complete on critical systems.

Best response: Ask the owner for the plan, date and risk.

Weaker responses: Accept the number; Demand 100% tomorrow; Ignore.

Common questions

Yes. Claiming the template and editing it are free.

The course itself is self-paced and online, and the live deck lets you add a live session. Whether online delivery meets your local rules depends on the law that applies to you, so check the rules that apply to you or ask your own counsel.

Annually, and when a regulation or major incident raises board attention.

Executives, board members and senior managers; run by L&D with the CISO or risk lead.

Record completion in your own LMS or record system, so you can show who finished the course and when. Check the retention period that applies to you in the rules that apply to you.

Your own details, each highlighted inside the course:
  • Who staff ask about security questions
  • Link to your information security policy
  • The route for reporting a security incident or suspected breach, and the time limit that applies
  • Your data protection officer or privacy lead
  • Link to the next course in your security awareness path
  • Where course completions are recorded
  • Link to the self-paced course
Then edit anything else you like: wording, scenarios, your logo.
Visit the help centre (opens in a new tab)